Risk. Compliance.
Audit Readiness.
Finally Connected.
Cyber and information-security governance for organisations in Ireland, the UK and the EU — and, since October 2026, the EU AI Act for the AI systems they use.
Vivid Risk helps organisations assess risk, stay audit-ready, simplify compliance, and make better business decisions.
Between them, scored controls are cited to 6 frameworks — NIS2, ISO 27001, DORA, NIST CSF 2.0, NCSC CAF, GDPR — each checked against its own published text, with CyFun Basic, Important and Essential coverage for Ireland and the EU. Every scored control in the core questionnaire carries its NIS2, ISO 27001, NIST CSF 2.0 and NCSC CAF citation, and its DORA or GDPR citation where it has one; the DORA-only questions cite DORA alone. The Cyber Resilience Act is covered separately, by an Article 14 reporting register for actively exploited vulnerabilities and severe incidents, with all six stage deadlines verified against the Official Journal. The EU AI Act is covered separately, by a register of the AI systems you use, a guided classification path for each system with the article behind every step, the duties that follow for your role with their citations and start dates, and the records the Act asks a deployer to keep. Serious-incident clocks run in the incident register.
- Understand your risk exposure
- Stay audit-ready year-round
- Prioritise what matters most
- Demonstrate compliance with confidence
Free account · see your score · pay only to unlock the report. How the free preview works
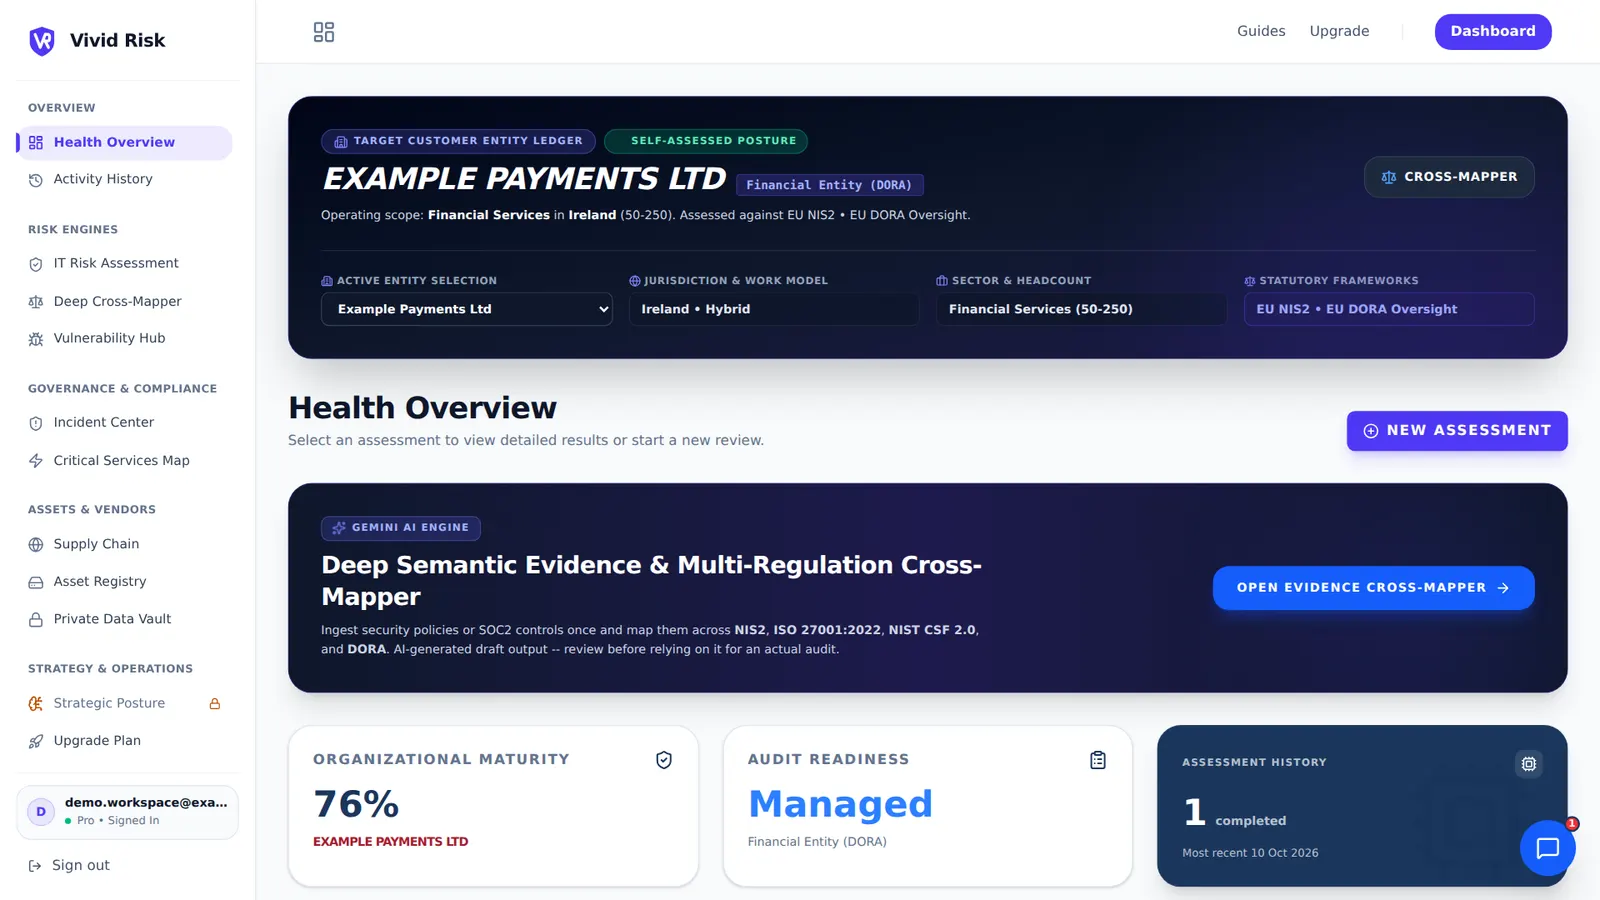
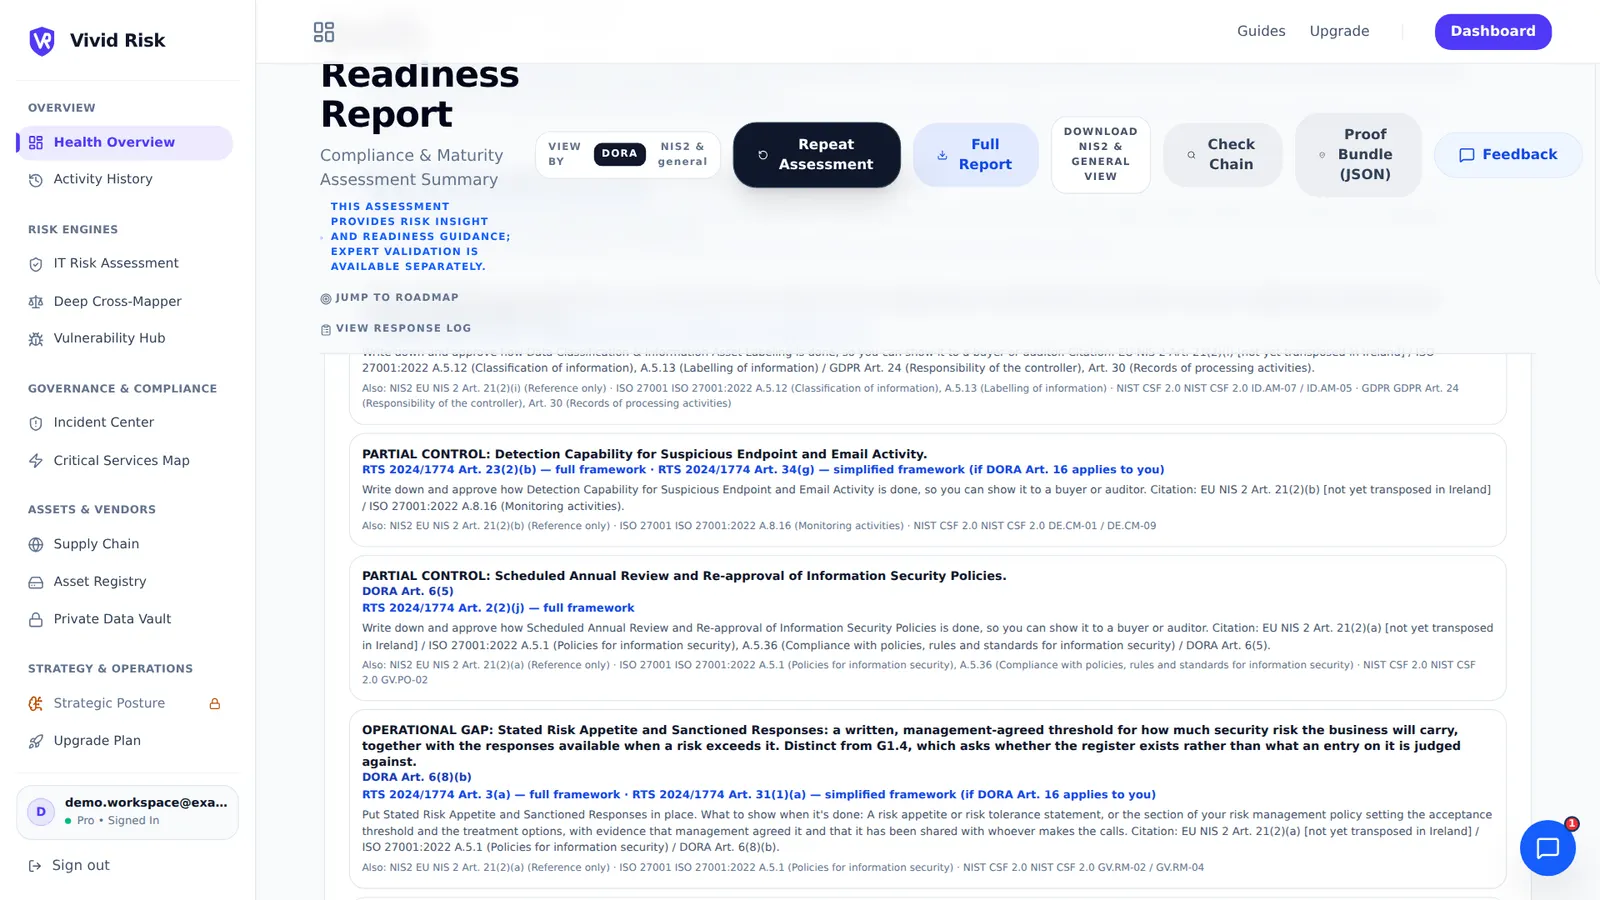
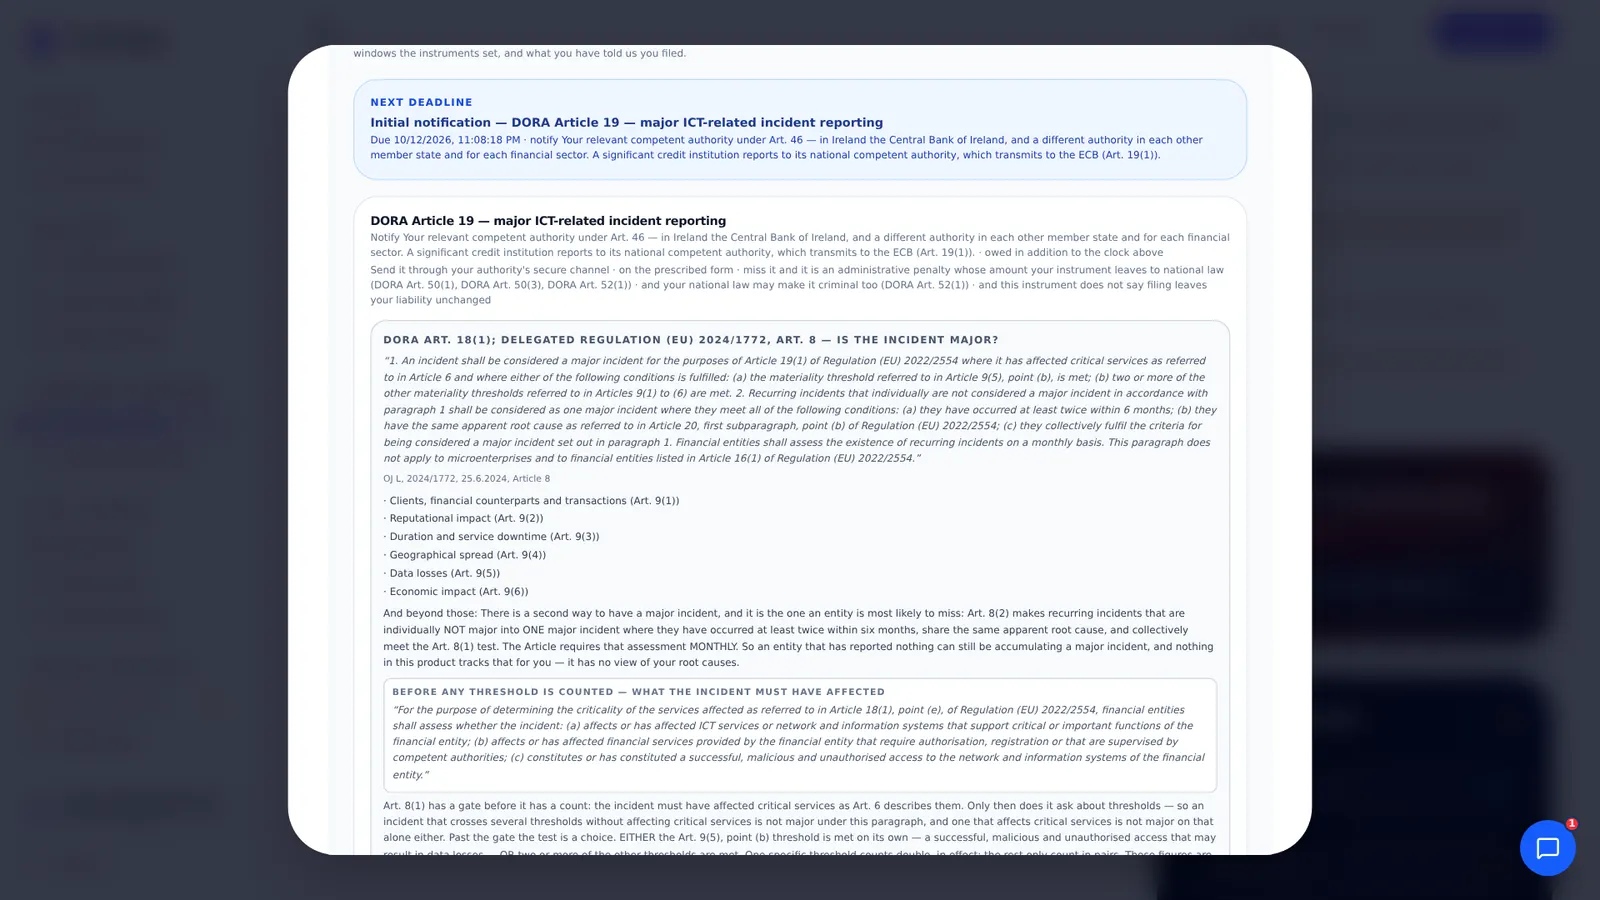
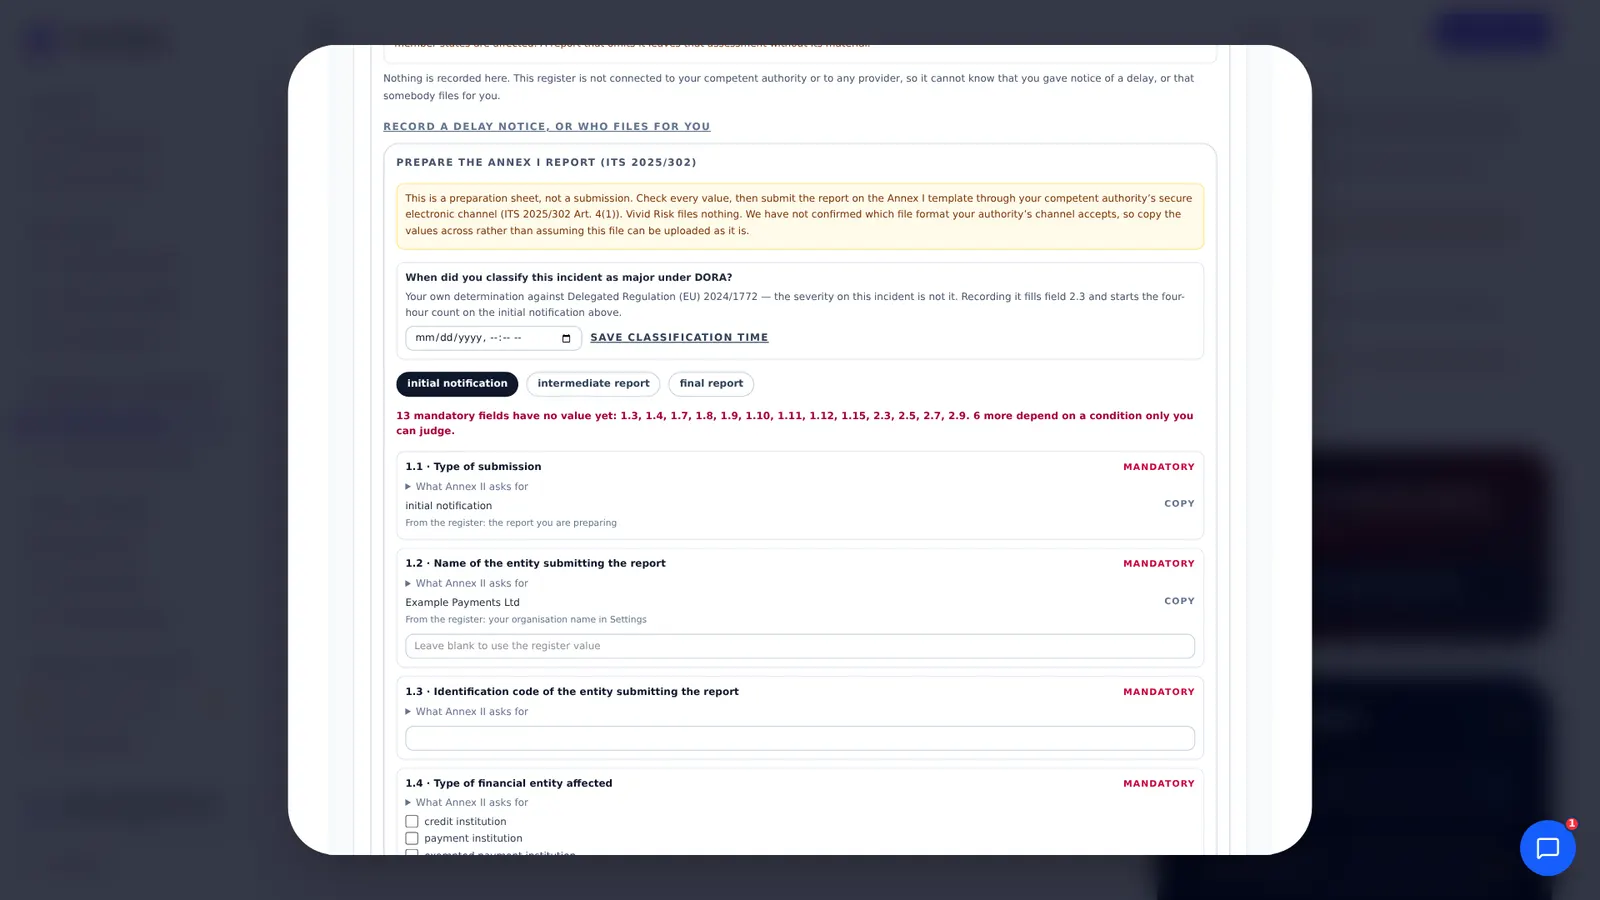
Inside the Compliance Workspace
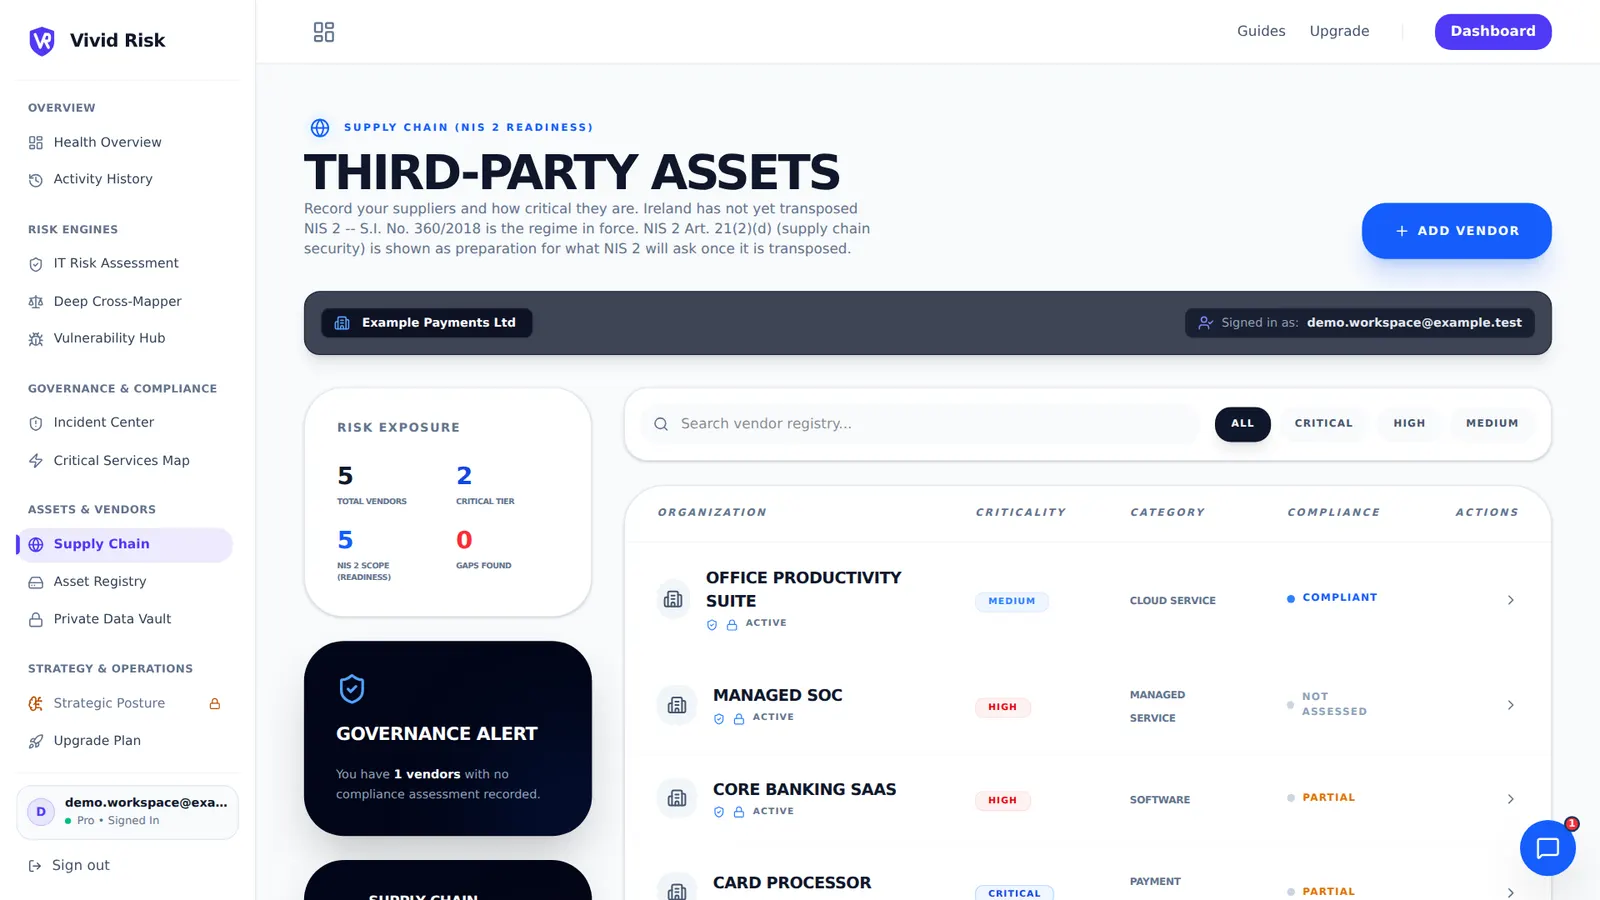
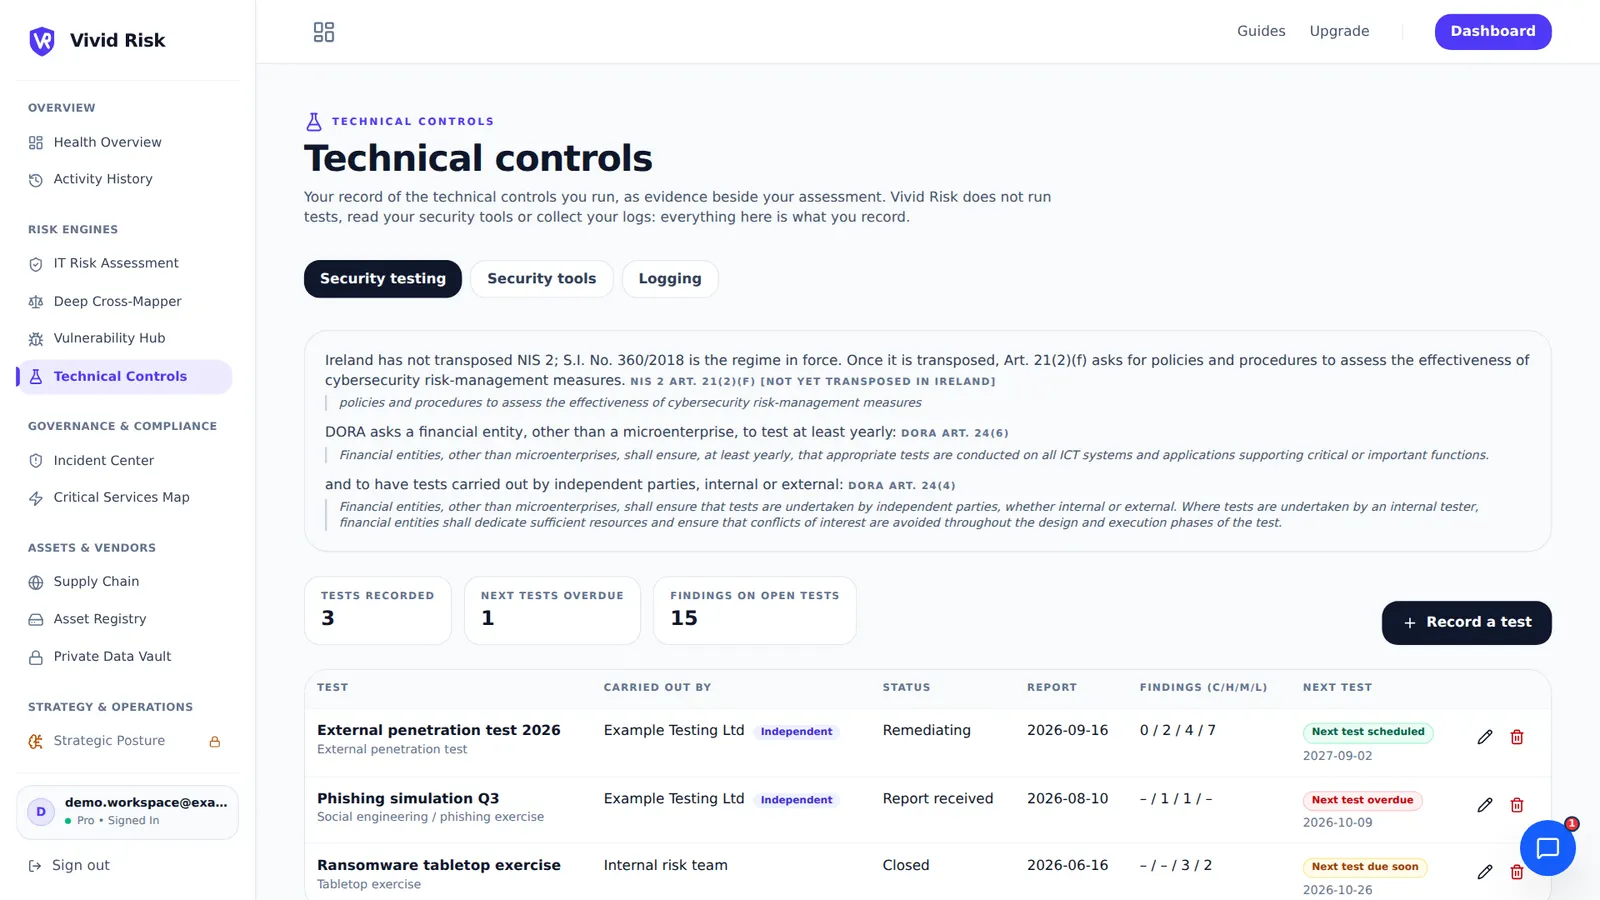
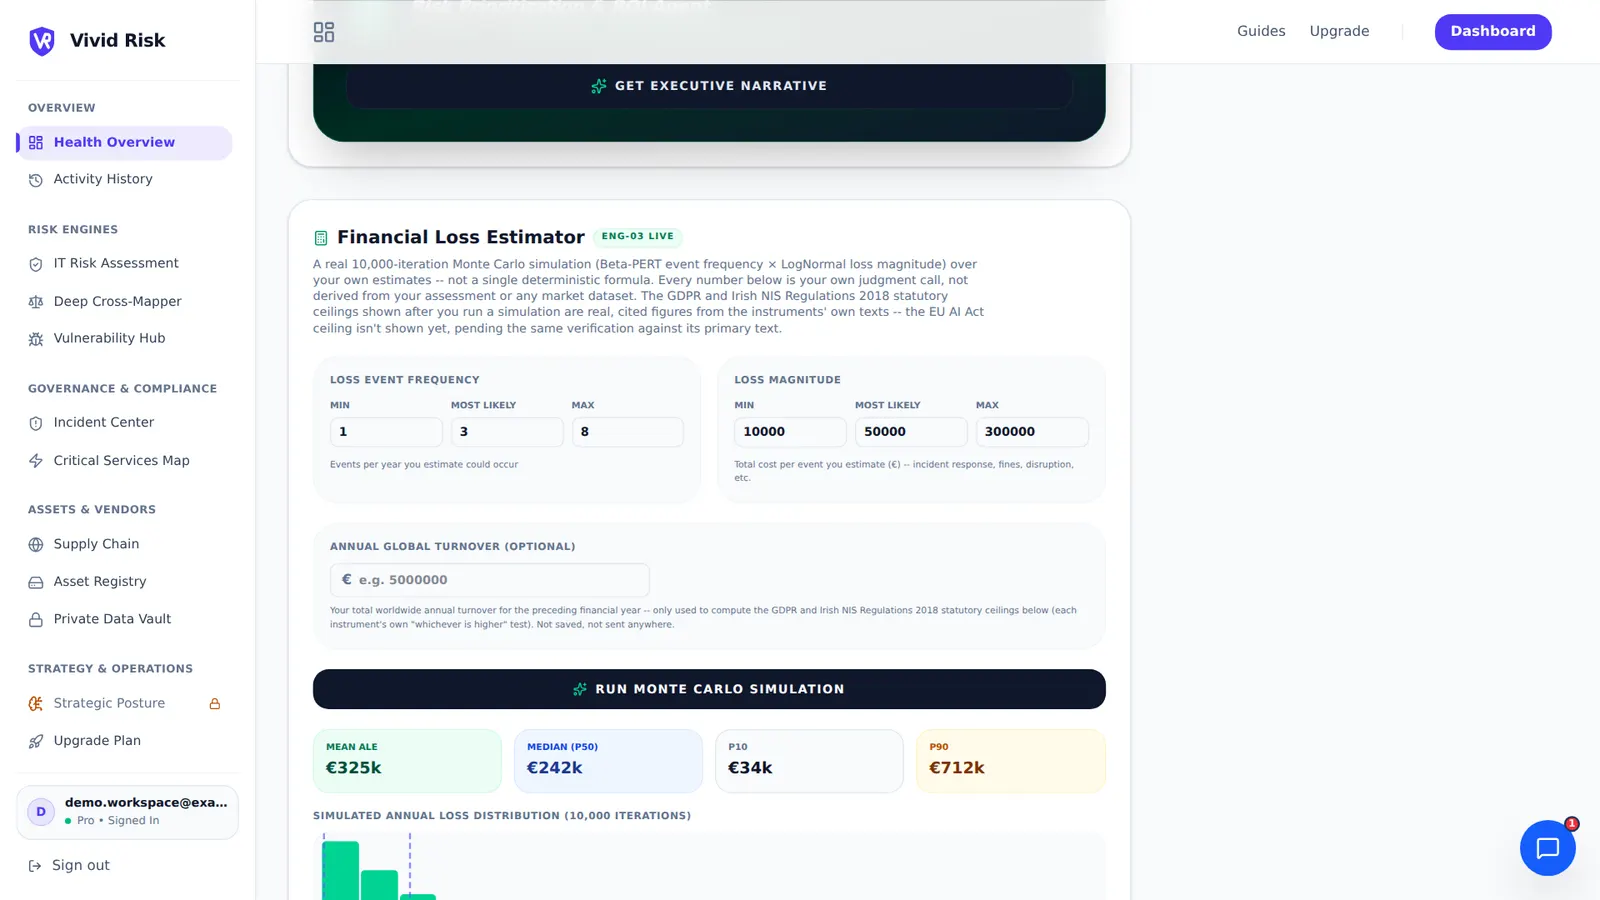
Real screens from the app. Example Payments Ltd, and everything recorded for it, is fictional demo data. See what the plan includes.
Why Organisations Choose
Vivid Risk
Most organisations have no shortage of data, reports, policies, or compliance activities.
What they lack is clarity.
“What are our biggest risks?”
“Are we audit-ready?”
“Which compliance gaps should we fix first?”
“What is the financial impact of those risks?”
“Which regulations apply to us?”
“How do we demonstrate compliance to auditors and regulators?”
One Platform. Multiple Challenges Solved.
Integrated modules designed to transform complex governance into streamlined, defensible outcomes.
IT Risk Assessment
Identify and assess risks across your organisation using structured frameworks and evidence-driven workflows.
- Risk visibility
- Gap identification
- Governance alignment
- Board-ready reporting
Audit Readiness
Move beyond reactive audits. Maintain structured evidence, track compliance activities, and stay prepared for audits throughout the year.
- Audit-ready documentation
- Evidence management
- Readiness between audits
- Reduced audit effort
Quantitative Risk Intelligence
Translate technical risks into business language. Understand potential financial exposure and prioritize investments where they deliver the greatest impact.
- Financial risk insights
- ROI-driven remediation
- Executive reporting
- Better decision-making
Regulatory Compliance
Manage multiple regulations from a single platform. Vivid Risk helps organisations navigate evolving regulatory requirements across Europe and globally.
- NIS2
- ISO 27001
- DORA
- NIST CSF 2.0
- NCSC CAF
- GDPR
- Cyber Essentials— indicative
- CyFun— indicative
- Cyber Resilience Act
- EU AI Act
- Digital Services Act— roadmap
What Vivid Risk is not
This is cyber and information-security governance. If you are looking for any of the following, we are the wrong tool and would rather you knew now.
Product safety, CE marking or conformity assessment
We cover the Cyber Resilience Act's incident and vulnerability REPORTING clock. We do not assess a product against essential requirements, produce technical documentation, or issue a Declaration of Conformity.
AI Act conformity assessment, certification or classification on your behalf
The AI Act workspace records the AI systems you use, shows what your answers indicate with the article behind each step, and keeps your records. The classification is yours; it certifies nothing, carries out no conformity assessment, and files nothing with anyone.
Manufacturing, machinery or workplace safety
Nothing here assesses physical process risk, machinery directives or occupational health and safety.
Financial, credit or market risk
The loss model quantifies the financial impact of CYBER events, from your own estimates. It is not a treasury, credit or market-risk tool.
ESG, quality or environmental management
No ISO 9001, no ISO 14001, no sustainability reporting.
An ISMS, or certification of any kind
We produce a self-assessed maturity score with cited controls and an evidence register. A certificate comes from an accredited body after an audit, and nothing here substitutes for one.
AI-Powered
Governance
Modern organisations need more than compliance tracking. They need governance they can keep current between audits.
Vivid Risk combines AI-assisted analysis with human oversight to help organisations:
- Track compliance readiness
- Prioritise risk reduction activities
- Manage regulatory obligations
- Prepare defensible audit trails
Deterministic logic and explainable AI models deliver consistent evidence trails verified against legal and technical standards.
What Makes Vivid Risk Different?
Most platforms simply track compliance items. Vivid Risk gives you an actionable intelligence layer.
- Understand Risk
- Prioritise Action
- Quantify Impact
- Demonstrate Readiness
- Support Executive Decisions
Risk as a Decision System
Traditional compliance tools focus on checklists.
Vivid Risk focuses on decisions.
Instead of simply showing compliance gaps, we help organisations understand:
- 01. PriorityWhat matters?
- 02. SequenceWhat to address first?
- 03. ExposureWhat is the business impact?
- 04. ActionWhat action to take next?
“Audit identifies the problem. Vivid Risk explains the cost and helps guide the response.”
Designed For
Purpose-built workflows tailored to the stakeholders driving governance, security, and assurance.
Small & Medium Businesses
Achieve compliance and improve governance without the complexity of enterprise GRC platforms.
Accessible • Fast SetupMSPs & MSSPs
Deliver scalable risk assessment, compliance, and audit-readiness services across multiple clients.
Multi-Tenant • High MarginAuditors & Advisors
Reduce manual effort, simplify evidence management, and accelerate engagements.
Cited Controls • AI-Drafted WorkpapersCISOs & Governance Teams
Gain visibility, defensibility, and confidence in your risk and compliance posture.
Executive Views • Score Trend
Our Vision
We believe governance should be an ongoing practice, grounded in evidence, and actionable.
Vivid Risk is building the next generation of Governance Intelligence, helping organisations understand risk, demonstrate compliance, and make better decisions — with AI governance support on our roadmap.
Ready to Transform Risk
Into Better Decisions?
See how Vivid Risk can help your organisation simplify compliance, improve audit readiness, and strengthen governance.